Agentic Payments Are Forcing a Redesign of Financial Control Layers
As software agents gain the ability to initiate payments, financial control is moving upstream into mandate design, consent, credential governance, liability and auditability.
Banks and payment companies are beginning to test a different kind of transaction flow.
The payment is not initiated directly by a person tapping a button or entering card details. A software agent can search, compare, select and initiate a transaction on the user’s behalf.
That changes the control problem.
The important question is not whether the agent can execute a payment quickly. The important question is what authority the agent is exercising, how that authority was granted, what limits apply and who remains accountable when the transaction produces an unexpected outcome.
Once execution authority can be delegated to software, governance becomes part of the payment architecture.
Execution authority has to be designed before it is automated
Traditional payment systems already contain delegated authority.
Companies give employees purchasing limits. Banks authorize standing instructions. Cardholders allow merchants to initiate recurring charges. Treasury teams operate within approval hierarchies.
Agentic payments extend this logic into a more dynamic environment.
A software agent may be asked to identify a supplier, choose between products, optimize price and complete a transaction. The user may not approve every individual step in real time.
That means the system needs a clear answer to several questions.
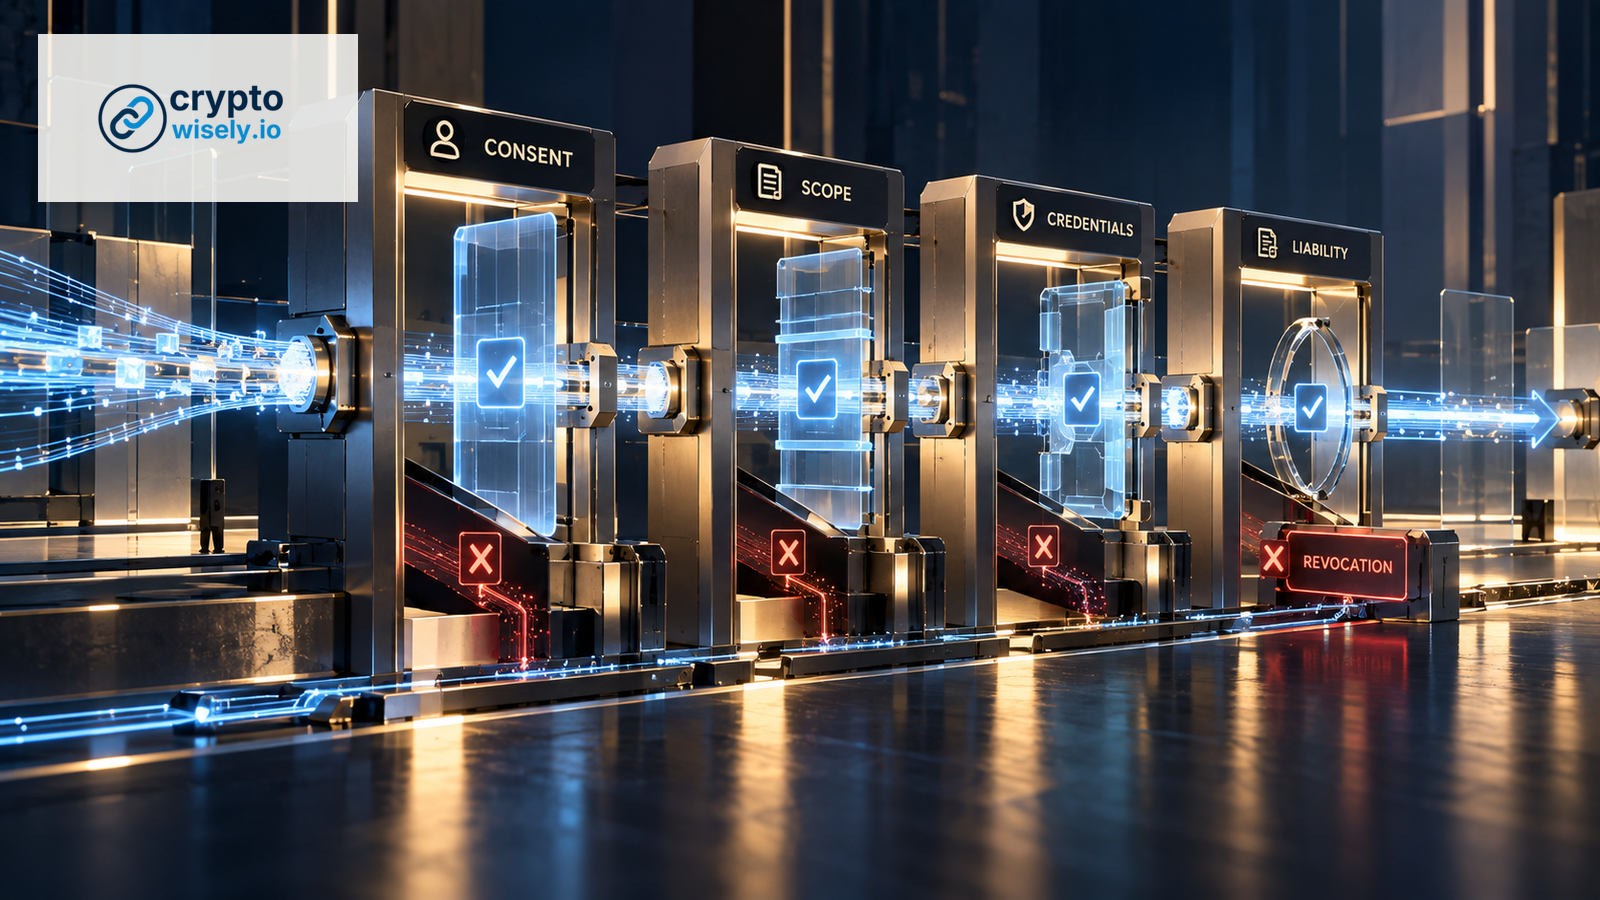
Who authorized the agent? What exactly was authorized? Which products, merchants or counterparties are permitted? What spending limits apply? How long does the mandate remain valid? Can the user revoke it immediately? What evidence is retained after the transaction?
The technology can automate the decision path.
It cannot eliminate the need to define the mandate.
Scope is the first control layer
An agent should not receive a vague instruction to spend money on behalf of a user or institution.
The scope needs to be explicit enough that both the system and the parties around it can understand what is permitted.
That can include transaction limits, merchant categories, jurisdictions, currencies, time windows, counterparty rules and product restrictions.
A corporate agent may be allowed to reorder approved supplies up to a specified amount but prohibited from creating a new vendor relationship. A consumer agent may be permitted to renew a subscription but not change the payment method without additional confirmation.
These boundaries matter because automated execution compresses decision time.
If the scope is poorly defined, the system discovers the ambiguity only after it begins acting.
Consent becomes an operating model
One-time approval is relatively simple.
Persistent delegated authority is more difficult.
The system needs to distinguish between a user approving one transaction and a user granting an agent an ongoing mandate. The second model requires clearer rules around duration, modification, revocation and evidence.
Consent also needs to remain understandable.
A technically valid authorization is weak if the user cannot tell what the agent is permitted to do. Institutions will need consent models that are granular enough for control but simple enough for people to manage.
Revocation is equally important.
If a user changes their mind, detects suspicious behavior or loses control of an account, the mandate needs to be suspended quickly across the systems that rely on it.
A delayed revocation mechanism turns delegated convenience into operational risk.
Credential ownership becomes strategically important
Agentic payments also raise questions about the credential used to execute the transaction.
The credential may be bank issued, network tokenized, device bound or generated specifically for an agentic workflow. Different models create different control points.
Who can issue the credential? Can the agent reuse it? Can it be moved to another device or environment? Does it identify the user, the agent, the mandate or all three? What happens when the underlying authorization changes?
Credential design therefore affects scalability.
A payment agent that acts through poorly governed credentials can create a new attack surface even if the payment network itself remains secure.
The stronger model is one in which the credential carries or references the limits of the mandate rather than behaving like unrestricted payment access.
Speed and verification remain a trade off
Automation creates pressure to reduce friction.
That is part of its value.
If every agentic action requires the same manual approval process as a conventional transaction, much of the efficiency disappears. But removing verification entirely shifts risk elsewhere.
The design problem is therefore not speed versus control.
It is deciding which controls should operate before execution, which can operate automatically during execution and which require escalation after an exception.
Low value transactions with familiar counterparties may justify a lighter path. High value transactions, new counterparties or unusual behavior may require stronger verification.
The control model can become adaptive.
What matters is that the trade off is explicit.
Liability does not disappear when decision making becomes automated
A failed or disputed transaction still needs an accountable party.
The presence of an agent introduces another layer into the sequence, but it does not remove responsibility from the institutions that designed, authorized or processed the activity.
Liability may depend on the nature of the failure.
Was the transaction inside the user’s mandate? Did the agent misinterpret the instruction? Was the credential compromised? Did the merchant provide inaccurate information? Did the bank or network process an instruction that should have been blocked?
These questions will matter for dispute handling, consumer protection and supervisory review.
A scalable model needs evidence that allows the transaction to be reconstructed after the fact.
Auditability is therefore not a reporting feature added later.
It is part of the execution architecture.
Measurement can reveal structural weakness early
Agentic payment systems will generate familiar performance metrics: approval rates, decline rates, fraud alerts, disputes, chargebacks and settlement exceptions.
Those metrics should not be viewed only as operational outputs.
They can reveal whether the mandate design itself is working.
A high decline rate may indicate that the agent is operating too close to the boundary of its permissions. A rise in disputes may show that users do not understand the authorization they granted. Repeated exceptions may indicate that the system is optimizing transaction completion while ignoring control quality.
Velocity can make a weak architecture appear successful for a short period.
Measurement discipline helps distinguish adoption from durable scalability.
Agentic payments move governance into the product
The important shift is not simply that software can pay.
The important shift is that execution authority can be delegated algorithmically.
That moves questions of consent, scope, credentials, revocation, liability and evidence into the product itself.
Institutions will not scale agentic payments simply because the experience appears intelligent or convenient.
They will scale them when the operating model is defensible.
The future of automated payments will depend as much on governance architecture as on software capability.